Direct evidence
Prompt, model, tool, endpoint, process, file, network, Git, browser, MCP, and session observations available from the integration.
Pavri correlates the available session, tool, endpoint, process, policy, and evidence context so analysts can understand what happened and what response followed.
Pavri investigations connect an alert to the implicated agent or assistant, session, user, endpoint, workspace, prompt, model, tool, process, policy decision, evidence source, and response record where the integration exposes those events.
Analysts should not have to infer whether an event is a direct observation, policy decision, human decision, response record, or analytical correlation.
Prompt, model, tool, endpoint, process, file, network, Git, browser, MCP, and session observations available from the integration.
Matched policy, reason, outcome, control point, timestamp, and evidence link.
Notification, containment, revocation, ticketing, policy change, or investigation action initiated after a decision or detection.
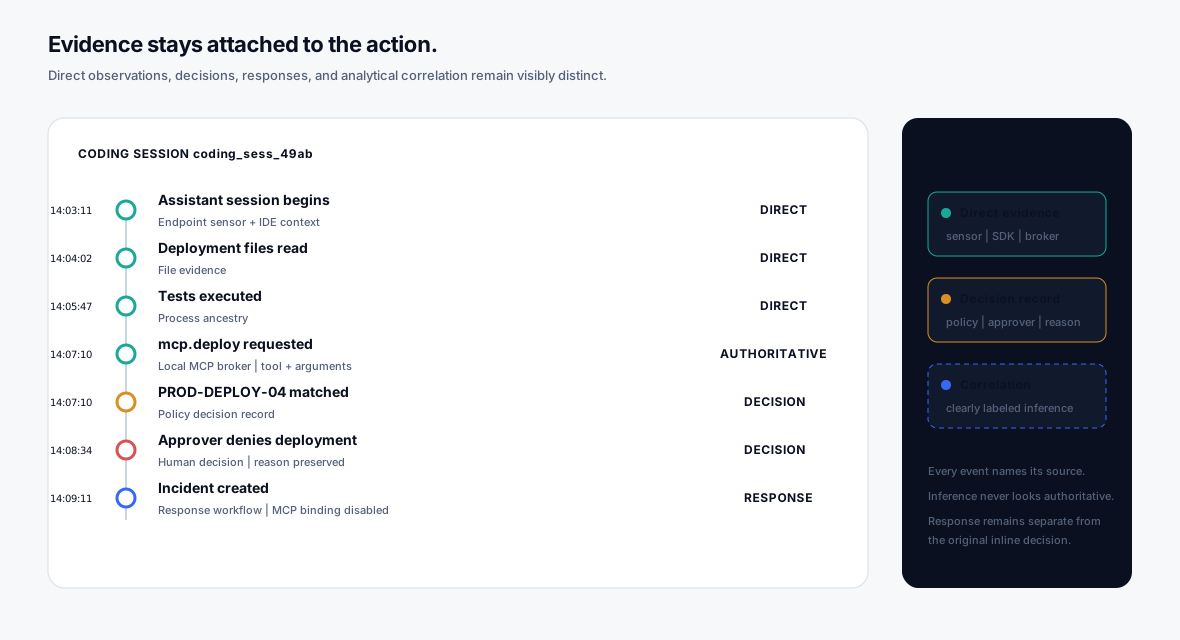
A Pavri investigation deep-links from an alert into the agent or assistant, user, endpoint, workspace, action chain, tool calls, policy decisions, detections, outcomes, and response history.
Use available evidence to understand what an agent did before, during, and after the alert.